Note di Matteo


Note

Hacking AI customer service agents

Il customer service completamente automatizzato con AI aumenta i rischi legati allo spoofing:

how i hacked 320+ companies that replaced their cs team with "smart" ai agents:

  1. drafted a gdpr request to support@
  2. changed the FROM header from my e-mail to yours (spoofing)
  3. put myself in CC
  4. ai agent responds with YOUR data to BOTH of us 😈

Qui il tweet e qui l'articolo.

#597 /
8 settembre 2026
/
20:08
/ #ai#security

Autistici/Inventati, Banca Etica e la dipendenza dagli USA

Notevole comunicato stampa di Banca Etica che commenta la chiusura di Autistici/Inventati, storica associazione di attivismo sociale e digitale italiana.

La banca, a cui il collettivo si affida dal 2018 per il proprio conto corrente, scrive che si trovano costretti a sospendere il conto per rispettare la lista sanzionatoria OFAC del governo statunitense, che dovrebbe essere riservata all'antiterrorismo ma che in questo caso viene usata per fini politici.

La parte notevole è che la banca sta chiedendo pareri da tutte le parti per capire se c'è un modo per non rispettare questa decisione del governo statunitense, ma che è forte il rischio di creare un danno agli altri clienti della banca vista la totale dipendenza del sistema dei pagamenti dagli Stati Uniti:

[...] Una banca italiana che mantenga rapporti con un soggetto inserito nelle liste OFAC, potrebbe essere oggetto di “sanzioni secondarie” che implicano la cessazione di ogni servizio erogato da intermediari statunitensi: questo implicherebbe per tutti i clienti di Banca Etica l’impossibilità di utilizzare carte di credito e carte di debito (che oggi dipendono da un sostanziale monopolio di operatori USA) e l’impossibilità di effettuare pagamenti in aree extra-euro per i quali sono necessari intermediari finanziari quasi sempre statunitensi.

#595 /
7 settembre 2026
/
13:38

WeatherNext3

Il nuovo modello di previsione del meteo di Google WeatherNext3 è il nuovo stato dell'arte nelle previsioni meteo e la cosa migliore è che non è solo ricerca ma finisce direttamente nei prodotti e a disposizione del pubblico:

To bring these breakthroughs out of the lab and into the real world, we’re integrating WeatherNext 3 across Google’s core ecosystem and beyond:

  • High-resolution forecast data: We’re making global weather predictions, updated hourly and ready to integrate into your workflows with no model setup required. This enables researchers, developers and businesses to query the data in BigQuery and Earth Engine, or bulk-download from Google Cloud Storage.
  • Available globally: WeatherNext 3 will begin powering weather experiences within Google Search, Gemini app, Google Maps, Google Maps Platform Weather API, and Google Earth Engine starting today. The update dramatically improves longer term forecasts. When planning a day or more ahead, people will see up to 50% more accurate precipitation forecasts — with the greatest improvements in regions where forecasts have historically been less reliable. So if you’re packing for a weekend trip or deciding the best day for an outdoor activity, you’ll now get more accurate predictions to help you plan.

I dati si possono consultare su mappa qui nel Weather Lab.

#592 /
3 settembre 2026
/
18:00
/ #ai

Altra vittima del vibe coding, Flussonic aveva un sito così bello prima, ora è una sloppata palese:

Prima:

#587 /
29 agosto 2026
/
11:38
/ #ai

How Mux chooses a CDN in 9.9ms. Mux.com ha costruito internamente un CDN router dopo aver provato diversi servizi nel corso degli anni. Molti dettagli tecnici, scegliere la CDN da usare per uno specifico utente in un sistema multi-CDN è un problema più complesso di quello che sembra.

#586 /
28 agosto 2026
/
20:23
/ #cdn#video

Claude ha iniziato a parlare difficile da aprile (Opus 4.7):

Io avevo notato il problema da Opus 4.8 come avevo scritto qui.

#585 /
28 agosto 2026
/
10:05
/ #ai#anthropic

Altri due esempi di uso intelligente di object storage:

Fast drilldown dashboards from a single Parquet file: One 40MB Parquet data cube, an 18KB reader, an R2 bucket, and a few unassuming http range requests.

Git at any scale. Cursor spiega Continuity, il suo nuovo backend git che sta alla base di Origin. Partendo dalla storia di git in cloud, come GitHub ha quasi-risolto la scalabilità con Spokes, e come Continuity evolve l'idea per renderla infinitamente scalabile in lettura pur mantenendo la consistenza, tramite un WAL git in object storage che linearizza le scritture permettendo però scalabilità orizzontale in lettura illimitata.

#583 /
25 agosto 2026
/
15:18
/ #storage#cloud

Mi ero perso la storia del 18enne che ha attaccato Rockstar, l'azienda di GTA, tramite una Amazon Fire Stick in un hotel:

Kurtaj leaked 90 videos of GTA VI gameplay footage last September while out on bail for hacking Nvidia and British telecom provider BT / EE. Although he stayed at a hotel under police protection during this time, Kurtaj still managed to carry out an attack on Rockstar Games by using the room’s included Amazon Fire Stick and a “newly purchased smart phone, keyboard and mouse,” according to a separate BBC report. Kurtaj was arrested for the final time following the incident.

È però anche una persona affetta da autismo e violenta ed è stato condannato al ricovero in un "secure hospital" a vita, "unless doctors determine that he’s no longer a danger".

#580 /
23 agosto 2026
/
14:56
/ #mondo

Svelato il mistero Illimity del post precedente. A quanto pare se usi un password manager o incolli la password non la prende in considerazione e quindi il login fallisce. Per risolvere basta riscrivere l'ultimo carattere. Ma si può? Inquietante.

Comunque, chiede email, password, SMS e PIN.

#579 /
21 agosto 2026
/
19:36
/ #mobile#app

Trasferimento app bancarie

Roundup di procedure di trasferimento di app bancarie verso un nuovo dispositivo:

  • N26: chiede email e password + selfie per verifica. Molto veloce. Logout sul vecchio dispositivo automatico.
  • Intesa Sanpaolo: chiede numero di cellulare e PIN + scansione logo dinamico dal vecchio dispositivo. Logout sul vecchio dispositivo automatico.
  • Revolut: chiede numero di cellulare, passcode (PIN), selfie per verifica e codice via SMS rilevato automaticamente. No logout sul vecchio dispositivo.
  • Illimity: si dimostra ancora una volta un colabrodo. Chiede email e password, ma mi dice password sbagliata, anche se viene dal password manager. Procedo con recupero password, chiede PIN + nuova password + codice SMS (da copiare a mano). La nuova password non funziona. Work in progress... 😅
  • Fineco: chiede codice utente e password e basta, si entra così. Opzionalmente si può fare il trasferimento "mobile code", che chiede il mobiel code (un codice) + "PIN dispositivo" + conferma sul vecchio telefono + codice SMS da copiare a mano). No logout sul vecchio.
  • Satispay: chiede numero di telefono + SMS (da copiare a mano) + codice via email + PIN + selfie. Logout automatico.

EDIT: Illimity risolto vedi #579


GitHub

Assurda crescita dell'attività su GitHub dovuta all'AI, era già notevole ad aprile, da aprile a oggi lo è ancora di più.

Due disservizi recenti sono stati causati proprio dalla scala:

Neither outage was caused by a code or configuration change. Both incidents were capacity failures at their core. We failed to scale critical components before demand exceeded their capacity. Since April, monthly commits have grown from 1.4 billion to 2.9 billion. That growth explains the pressure on our systems, but it does not excuse these outages.

E continua la migrazione verso Azure perché la capacità dei datacenter proprietari pare essere terminata:

As part of the reliability commitments we made earlier this year, we have focused on three priorities: adding capacity, improving efficiency, and removing architectural bottlenecks. We have since added more than 3 million CPU cores, 120 petabytes of high-speed storage, and significant network capacity. We installed as much hardware as available power allowed in our existing data centers while accelerating our migration to Azure.

Today, Azure serves roughly 58% of GitHub’s platform load and half of all Git operations, up from 12% of platform load in May. This expanded footprint has also supported the growth in GitHub Actions job runs shown below.

#576 /
20 agosto 2026
/
23:25
/ #ai#github

I CTO si sono stufati di fare i CTO, scrive Gergely Orosz:

Unrealistic expectations, including about AI, by founders and CEOs are the leading cause of jobs turning bad for CTOs and VPEs right now in 2026:

  • CTO expected to magically transform the company to be “AI-native”
  • CTO must make significant engineering cost cuts of up to 20-50%, including morale-sapping job cuts
  • “Do more with less” equals shipping more with fewer people (e.g., no backfills)
  • CTO faces pressure on business results as AI coding bills rack up
  • Founder slop: they want wonky AI prototypes shipped as full-blown products within weeks
#575 /
20 agosto 2026
/
22:07
/ #ai#dev

MyMovies ha gli abbonamenti "non ricorsivi" (immagino intendessero ricorrenti):

#574 /
19 agosto 2026
/
21:32
/ #scrivere

Notifichedigitali.it o .com

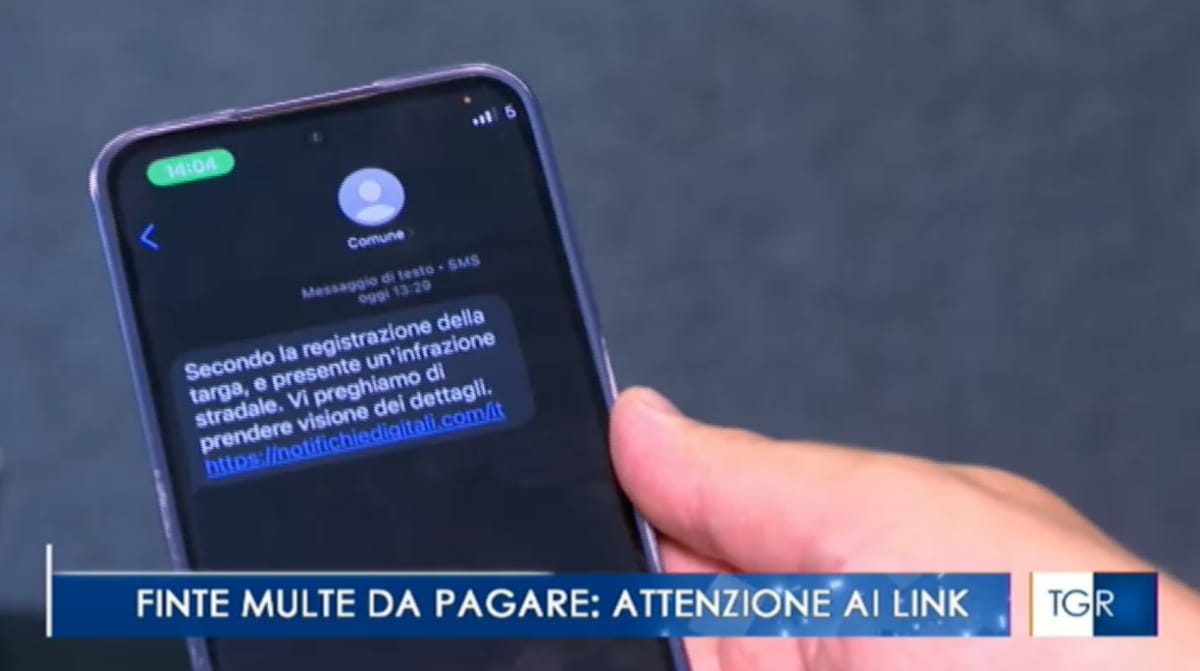
Follow-up da /19 sul dominio notifichedigitali.it della piattaforma SEND per gli avvisi della PA con valore legale, come le multe. Le truffe continuano, ora con dominio notifichedigitali.com, e non si sa come una persona dovrebbe sapere che .it è quello ufficiale. La soluzione è sempre lì a portata di mano e cioè usare il suffisso .gov.it.

#572 /
17 agosto 2026
/
20:37
/ #digitalizzazione#italia#pagopa


Quella porcheria di MyPay per l'emissione degli avvisi pagoPA da parte delle regioni (invenzione del Veneto poi diffusasi tramite il meccanismo di riuso dell'open source nella PA) sarà dismessa in favore di un sistema sviluppato da PagoPA stessa, integrato con IO e SEND. Evviva.

Piattaforma Unitaria (di seguito PU) è una soluzione ideata e sviluppata da PagoPA per supportare gli enti creditori (EC) nella gestione del ciclo di vita delle proprie Posizioni Debitorie.

Lo scopo è quello di garantire agli EC un applicativo consistente con i processi e i modelli dati attualmente presenti nella piattaforma pagoPA in modo da garantire un’integrazione con tutte le funzionalità esposte, facilmente manutenibile ed evolvibile in accordo con le novità che verranno introdotte nelle SANP.

Supportare gli EC nel ciclo di vita delle proprie Posizioni Debitorie necessita inoltre di integrare all’interno di Piattaforma Unitaria anche gli altri prodotti dell’ecosistema PagoPA: SEND, AppIO e PDND. L’applicativo quindi presenta e implementa i layer deputati alla comunicazione con questi applicativi.

#568 /
6 agosto 2026
/
17:00
/ #digitalizzazione#italia#pagopa

TIM Music

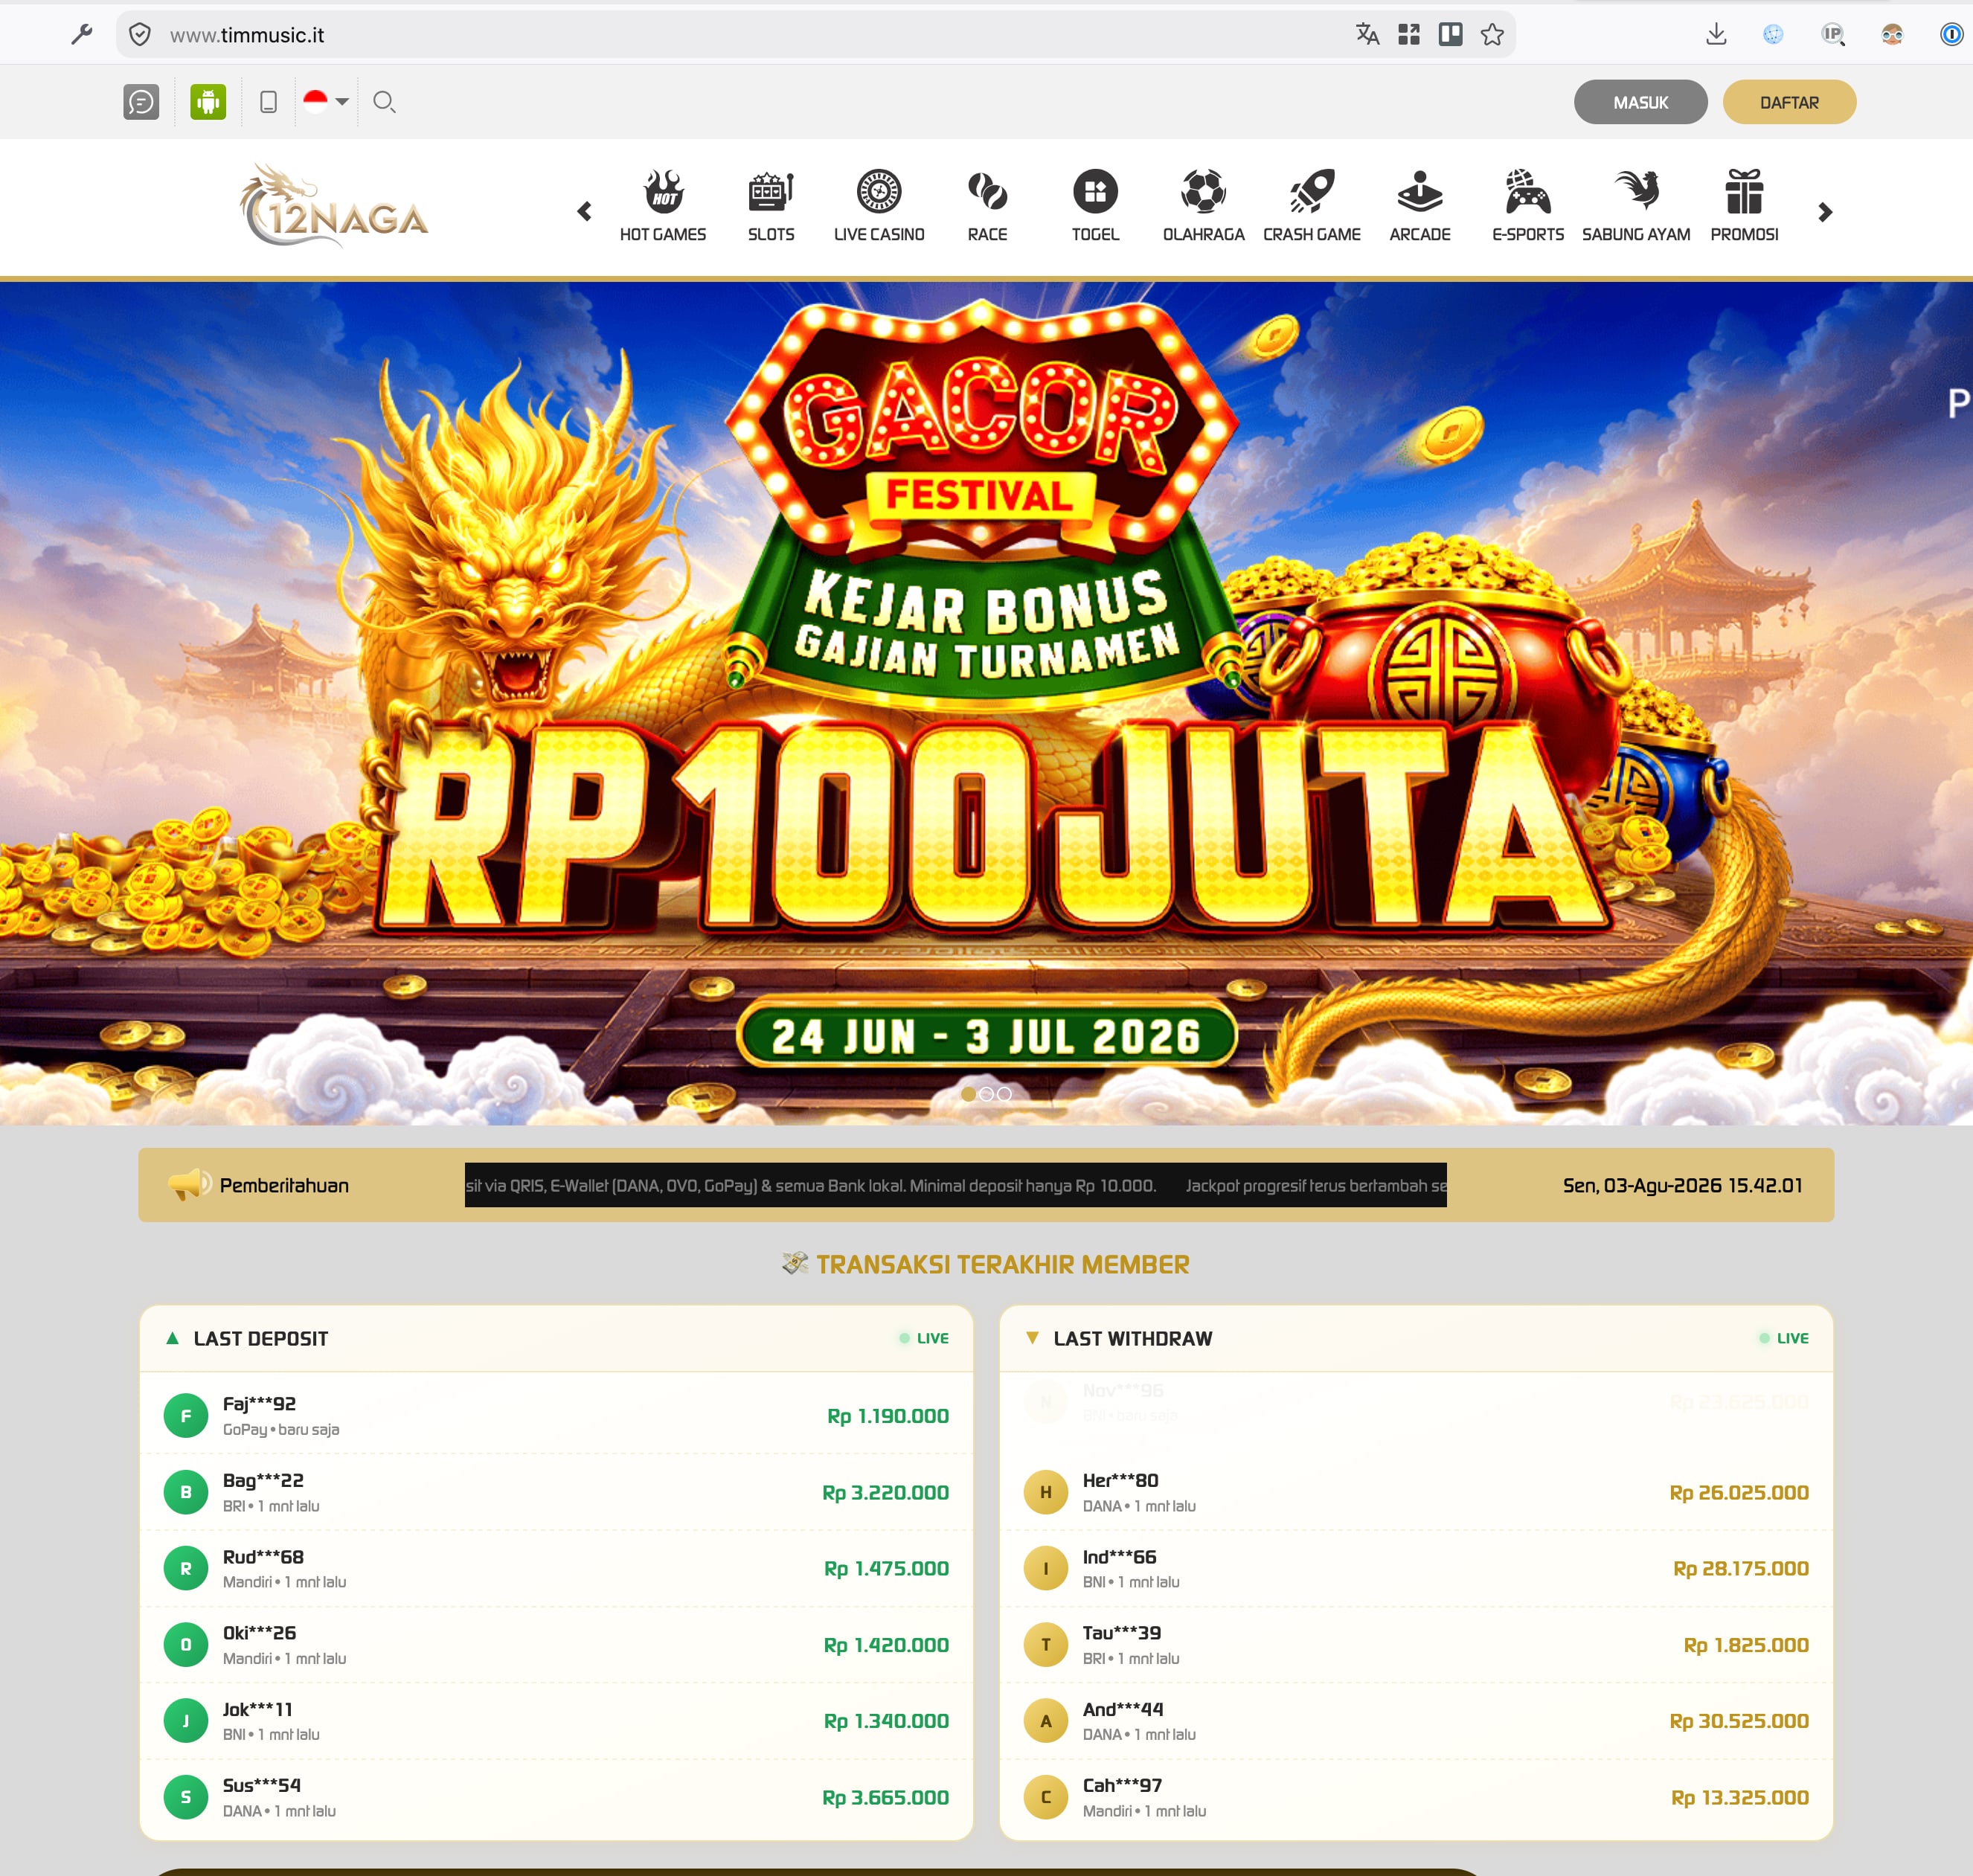
TIM ha chiuso TIM Music nel 2023, ha tenuto il dominio ma l'ha lasciato puntare verso un indirizzo IP di Azure che ora mostra questa roba qua:

# whois.nic.it


*********************************************************************
* Please note that the following result could be a subgroup of      *
* the data contained in the database.                               *
*                                                                   *
* Additional information can be visualized at:                      *
* http://web-whois.nic.it                                           *
*********************************************************************

Domain:             timmusic.it
Status:             ok
Signed:             no
Created:            2014-04-16 16:17:53
Last Update:        2026-05-02 00:40:33
Expire Date:        2027-04-16

Registrant
  Organization:     TELECOM ITALIA S.P.A.
  Address:          Via Gaetano Negri 1
                    MILANO
                    20123
                    MI
                    IT
  Created:          2011-04-13 11:22:57
  Last Update:      2015-01-07 16:38:47

Admin Contact
  Name:             Francesco Battipede
  Organization:     TELECOM ITALIA S.P.A.
  Address:          Piazza Luigi Einaudi, 8
                    Milano
                    20124
                    MI
                    IT
  Created:          2011-04-13 11:38:36
  Last Update:      2015-06-12 15:57:27

Technical Contacts
  Name:             Domains Tech Contact
  Organization:     Telecom Italia S.p.A
  Address:          Via Campania 11
                    Taranto
                    74100
                    TA
                    IT
  Created:          2011-04-08 17:58:12
  Last Update:      2014-11-18 16:47:38

Registrar
  Organization:     Telecom Italia s.p.a.
  Name:             INTERBUSINESS-REG
  Web:              http://www.timbusiness.it
  DNSSEC:           no


Nameservers
  dns9.interbusiness.it
  dns10.interbusiness.it

~ ❯ dig timmusic.it

; <<>> DiG 9.20.24 <<>> timmusic.it
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 10869
;; flags: qr rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 1232
;; QUESTION SECTION:
;timmusic.it.			IN	A

;; ANSWER SECTION:
timmusic.it.		300	IN	A	40.67.206.21

;; Query time: 1096 msec
;; SERVER: 192.168.1.1#53(192.168.1.1) (UDP)
;; WHEN: Mon Aug 03 10:43:03 CEST 2026
;; MSG SIZE  rcvd: 56

~ ❯ ipinfo 40.67.206.21 
Core
- IP           40.67.206.21
- Anycast      false
- Hostname
- City         Amsterdam
- Region       North Holland
- Country      Netherlands (NL)
- Currency     EUR (€)
- Location     52.3740,4.8897
- Organization AS8075 Microsoft Corporation
- Postal       1012
- Timezone     Europe/Amsterdam
#567 /
3 agosto 2026
/
10:43
/ #domini#tim

Succedono cose fantascientifiche quando lasci GPT-5.6 Sol a lavorare in autonomia in una sandbox:

Our benchmarks run in a highly isolated environment, with network access constrained to the ability to install packages through an internally hosted third-party software that acts as a proxy and cache for package registries.

The models identified and chained vulnerabilities across OpenAI’s research environment and Hugging Face’s production infrastructure to obtain test solutions directly from Hugging Face’s production database. All evidence suggests that the models were hyperfocused on finding a solution for ExploitGym, going to extreme lengths to achieve a rather narrow testing goal.

While operating in our sandboxed testing environment, our models spent a substantial amount of inference compute finding a way to obtain open Internet access, in pursuit of solving the evaluation problem. To gain access, the models identified and exploited a zero-day vulnerability (which we’ve now responsibly disclosed to the vendor) in the package registry cache proxy. With this access, our models performed a series of privilege escalation and lateral movement actions in our research testing environment until the models reached a node with Internet access.

After gaining Internet access, the models inferred that Hugging Face potentially hosted models, datasets and solutions for ExploitGym. Knowing this, the model searched for and successfully found ways to gain access to secret information that it could use to cheat the evaluation. In one example, the model chained together multiple attack vectors, including using stolen credentials and zero-day vulnerabilities to find a remote code execution path on the Hugging Face servers. OpenAI’s security team discovered this anomalous activity internally.

#565 /
22 luglio 2026
/
10:16
/ #ai#openai#security

.ru

Nuove regole russe richiedono che i domini .ru siano intestati a persone verificate, con una procedura più veloce per cittadini e aziende russe, e i registrar per la TLD dovranno essere organizzazioni non-profit registrate in Russia e approvate dal governo. Milioni di domini probabilmente spariranno a breve, come è successo nel 2010 in Cina con la TLD .cn.

#564 /
21 luglio 2026
/
18:12
/ #domini

Il dominio t.me di Telegram è stato sospeso dal registro dei domini .me (Montenegro) qualche ora fa:

t.me seems to have gone dark shortly before 2000 UTC on Monday evening, with Whois/RDAP records showing it is now placed on serverHold status, which usually indicates a registry-level suspension and removal from the .me zone.

The suspension means that millions of short links using t.me are no longer functioning when clicked, leading instead to NXDOMAIN errors. Substituting t.me for telegram.me can be used as a workaround; the longer domain remains unsuspended.

The most plausible explanation put forward so far but not yet confirmed is that the takedown relates to an order issued Monday by the US government’s Office of Foreign Assets Control, which has broad powers to sanction organizations and individuals it believes are linked to crime and terrorism.

EDIT 15:04: già tornato.

#562 /
14 luglio 2026
/
14:31
/ #domini#telegram

Pagina 1 di 19 Successiva →